> ## Documentation Index
> Fetch the complete documentation index at: https://docs.slm.m1amdocs.com/llms.txt
> Use this file to discover all available pages before exploring further.
# Setting up Okta Authentication
* It is recommended that the set up of your Okta account and application be performed twice:
1. Okta staging > Vindicia Subscribe Staging
2. Okta Production > Vindicia Subscribe Production
* Okta passwords must meet PCI requirements. See [External User Authentication Requirements](externalUserAuthenticationRequirements) for details.
* Multi-factor Authentication and re-authentication is required for this implementation. See [External User Authentication Requirements](externalUserAuthenticationRequirements) for details.
1. In your Okta org account, navigate to **Applications** > **Applications**.
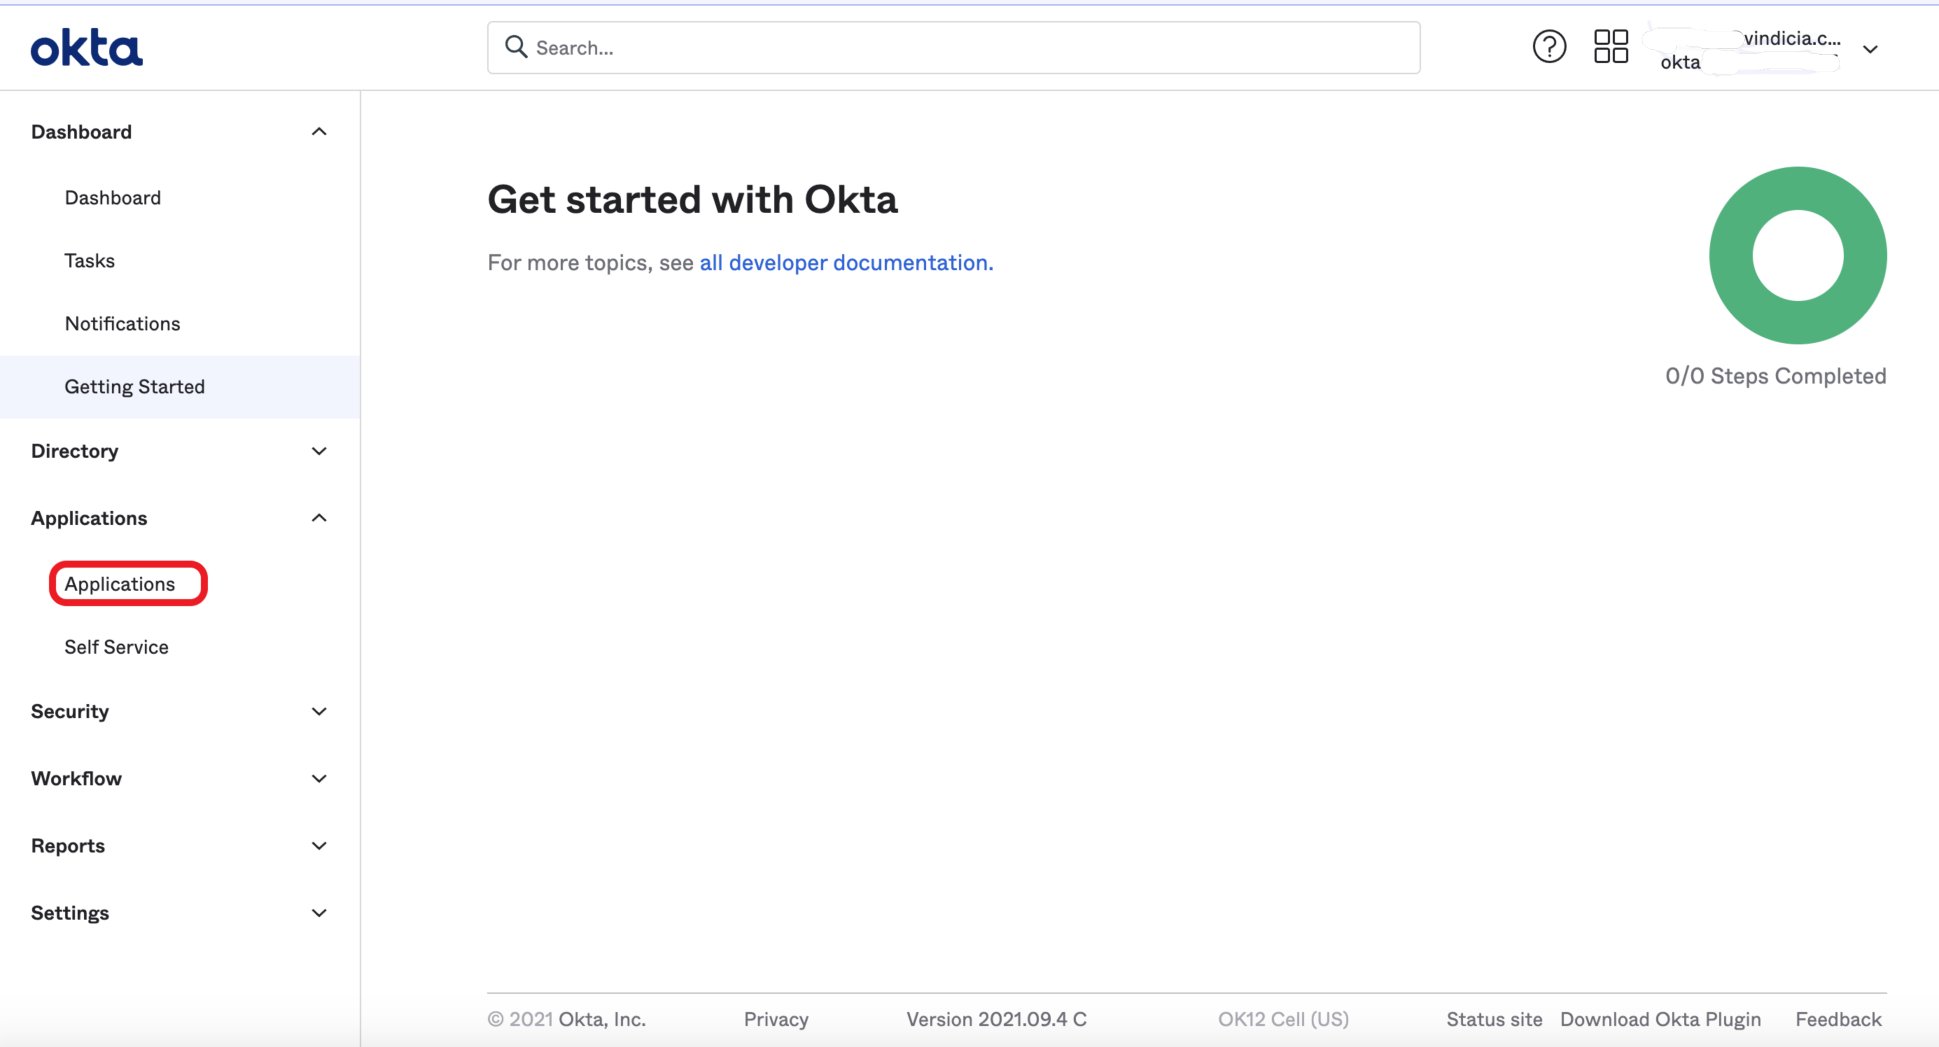 2. Click the **Create App Integration** button.
The **Create a new app integration** screen appears.
3. Define as follows:
1. For **Sign-in method**, select **OIDC - OpenID Connect**.
2. For **Application type**, select **Web Application**.
3. Click **Next**.
The **New Web App Integration** screen appears.
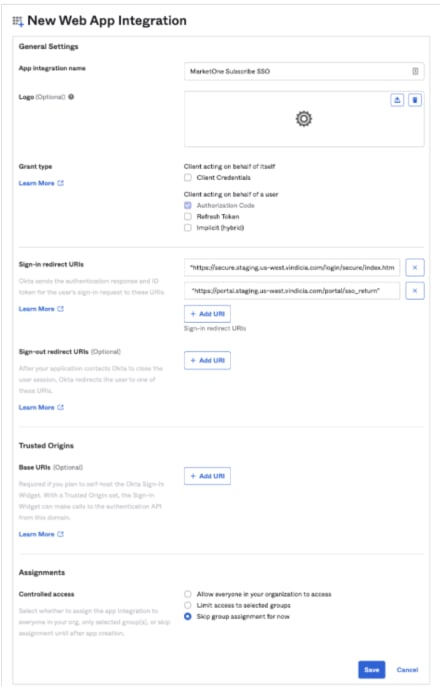
4. Define the New Web App Integration as follows:
1. For **App integration name**, enter the name you'd like to give this app. For example, use **Vindicia Subscribe**.
2. For **Grant type**, select **Authorization Code**and ensure that all other checkboxes are clear.
3. For **Sign-in redirect URIs**, enter the following as relevant for either your production or staging implementation:
* **Staging**:
* Subscribe Portal 2.0 staging: [https://portal.staging.us-west.vindicia.com/portal/sso\_return](https://portal.staging.us-west.vindicia.com/portal/sso_return)
* **Production**:
* Subscribe Portal 2.0 production: [https://portal.vindicia.com/portal/sso\_return](https://portal.vindicia.com/portal/sso_return)
4. For **Sign-out redirect URI**, leave blank.
5. For **Trusted Origins**, leave blank.
6. For **Assignments**, limit access to the relevant groups in your organization that require access to Vindicia Subscribe.
 5. Click **Save**.
The new Web integration App is saved.
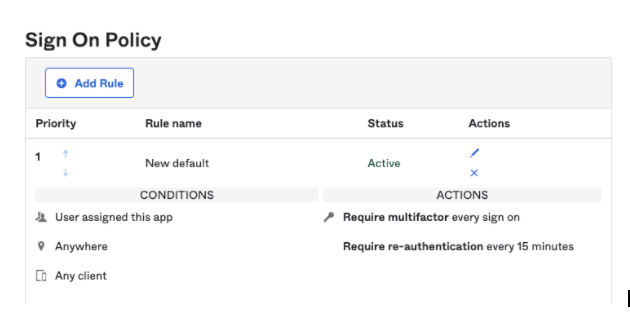
6. In the newly created web integration app, access the **Sign On** tab and set the following recommended options:
1. click **Add Rule**.
2. Set **Require multifactor** every sign on and **Require re-authentication** every 15 minutes.
 7. In the newly created web integration app, access the **General** tab and note the required details to pass to Vindicia.
1. Copy the following details from the Client Credentials and General Settings panes and save them to a .txt file.
* Client ID
* Client secret
* Okta domain
2. Encrypt the file and pass it to your Vindicia contact point for integration.
8. In Subscribe Portal 1.0, access Reports and run the **Merchant Users** report with **User Status** set to Active.
1. Ensure that all the users that require access to Subscribe appear in the report with a corresponding email address.
2. Ensure that the users' emails in the report match the emails used in Okta.
9. To test the successful setup, access Subscribe Merchant Portal 2.0 at [https://portal.staging.us-west.vindicia.com/](https://portal.staging.us-west.vindicia.com/portal/sso_return) and enter your username.
You are redirected to to your Okta sign in page for authentication.
 **Parent topic:**[External User Authentication in Vindicia](../topics/externalUserAuthenticationAbout)
This documentation is built and hosted on [Mintlify](https://mintlify.com), a developer documentation platform.