> ## Documentation Index
> Fetch the complete documentation index at: https://docs.slm.m1amdocs.com/llms.txt
> Use this file to discover all available pages before exploring further.
# Setting up Azure AD (Active Directory) Authentication
* The [External User Authentication Requirements](externalUserAuthenticationRequirements) must be met as part of this procedure.
* It is recommended that the set up of your Azure account and application be performed twice:
1. Azure staging > Vindicia Subscribe Staging
2. Azure Production > Vindicia Subscribe Production
1. Register a new App as follows:
1. Log in to your Azure account and navigate to **Azure Active Directory** > **App registrations**.
2. Create a new application by selecting **+ New registration**.
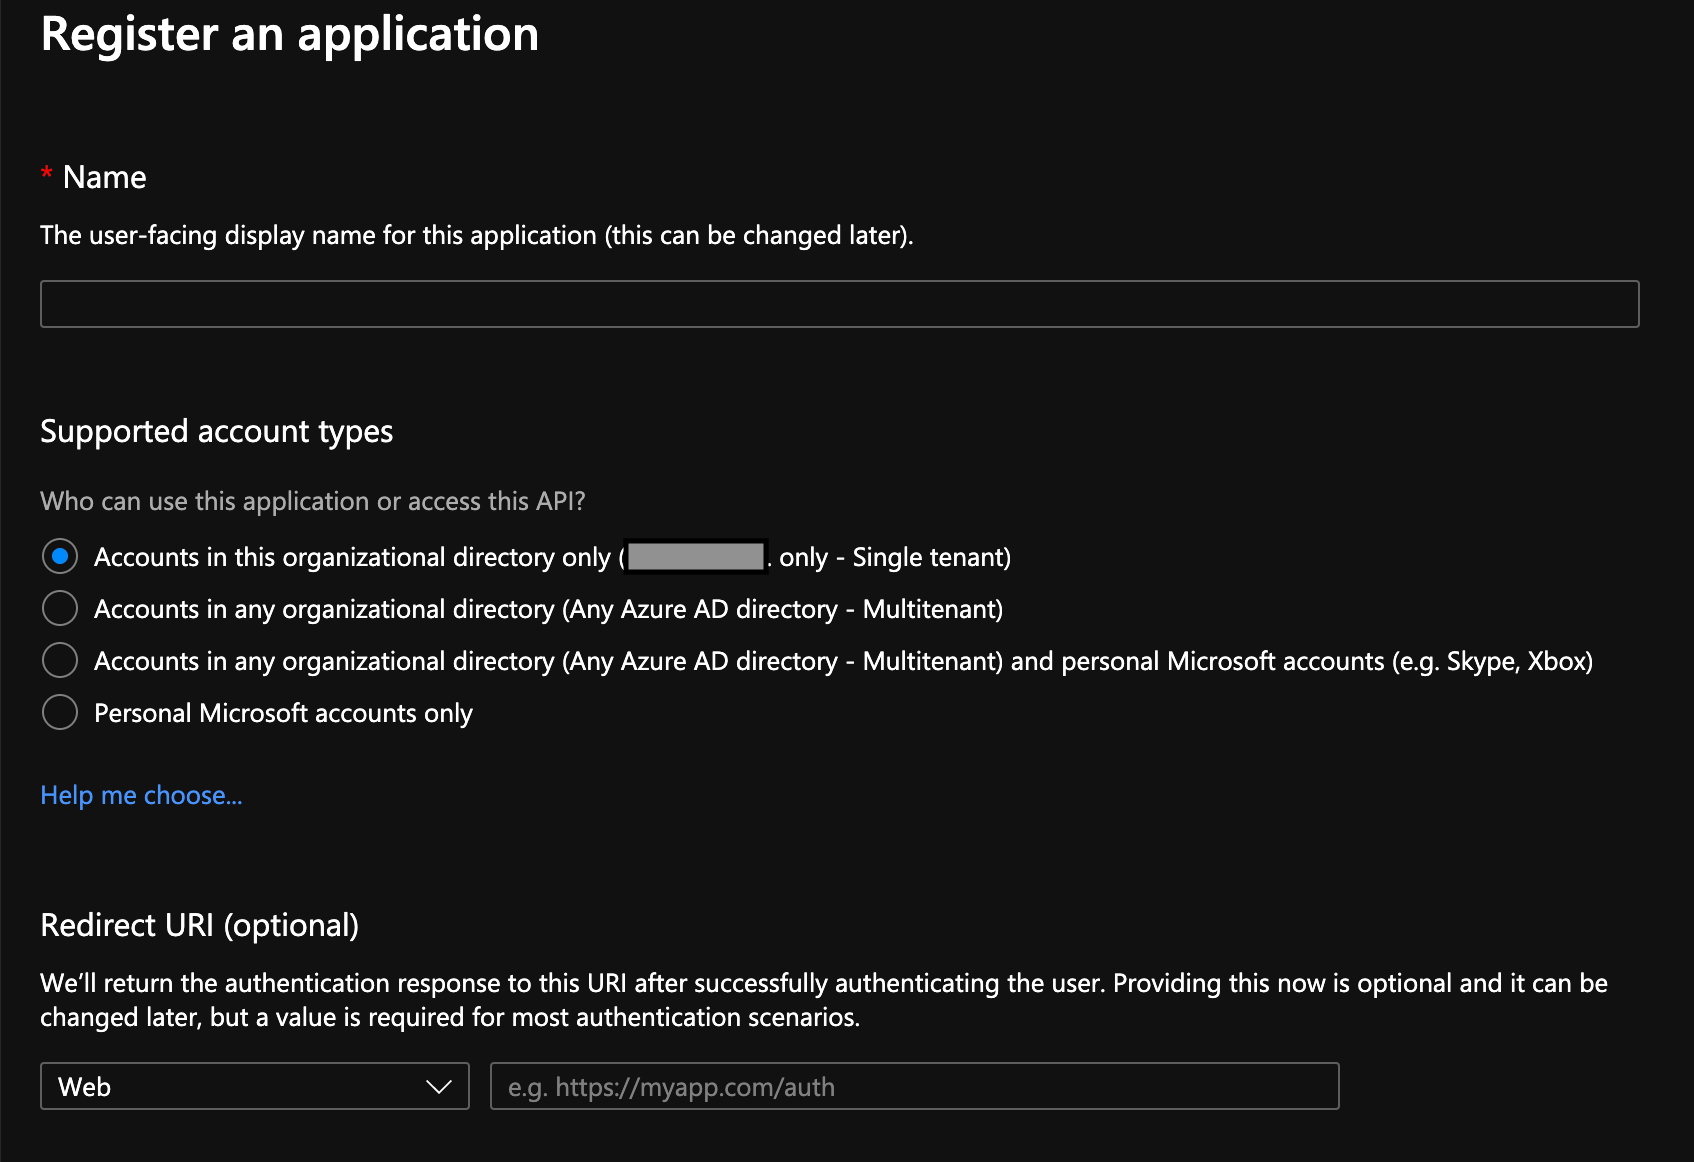 3. Enter a **Name**.
4. Select a **Supported account types** option. Consult your security organization and the Azure documentation. Record this choice because your OIDC Discovery Metadata URL depends on this choice.
5. Leave the **Redirect URI (optional)** field blank. You'll provide this information later.
6. Click **Register**.
The application configuration **Overview** page appears.
2. Generate a Relying Party OAuth Client Secret on the **Overview** page as follows:
1. Click **Certificates & secrets**.
The **Certificates and Secrets** page appears.
2. Click **+ New client secret**.
The **Add a client secret** panel appears
3. Provide a **Description** and an **Expires** length that follows your security organization’s guidelines in the **Add a client secret** panel.
4. Click **Add**.
5. Copy the **Value** corresponding to the newly-created client secret into a .txt file.
This is the **Relying Party OAuth Client Secret** that you will configure with Vindicia later.
**Note:** Any changes made to the Client Secret value must be communicated with Vindicia Client Technical Support.
3. Configure the Redirect URIs as follows:
1. Click the **Overview** tab.
2. Click **Add a Redirect URI**.
The **Authentication** page appears.
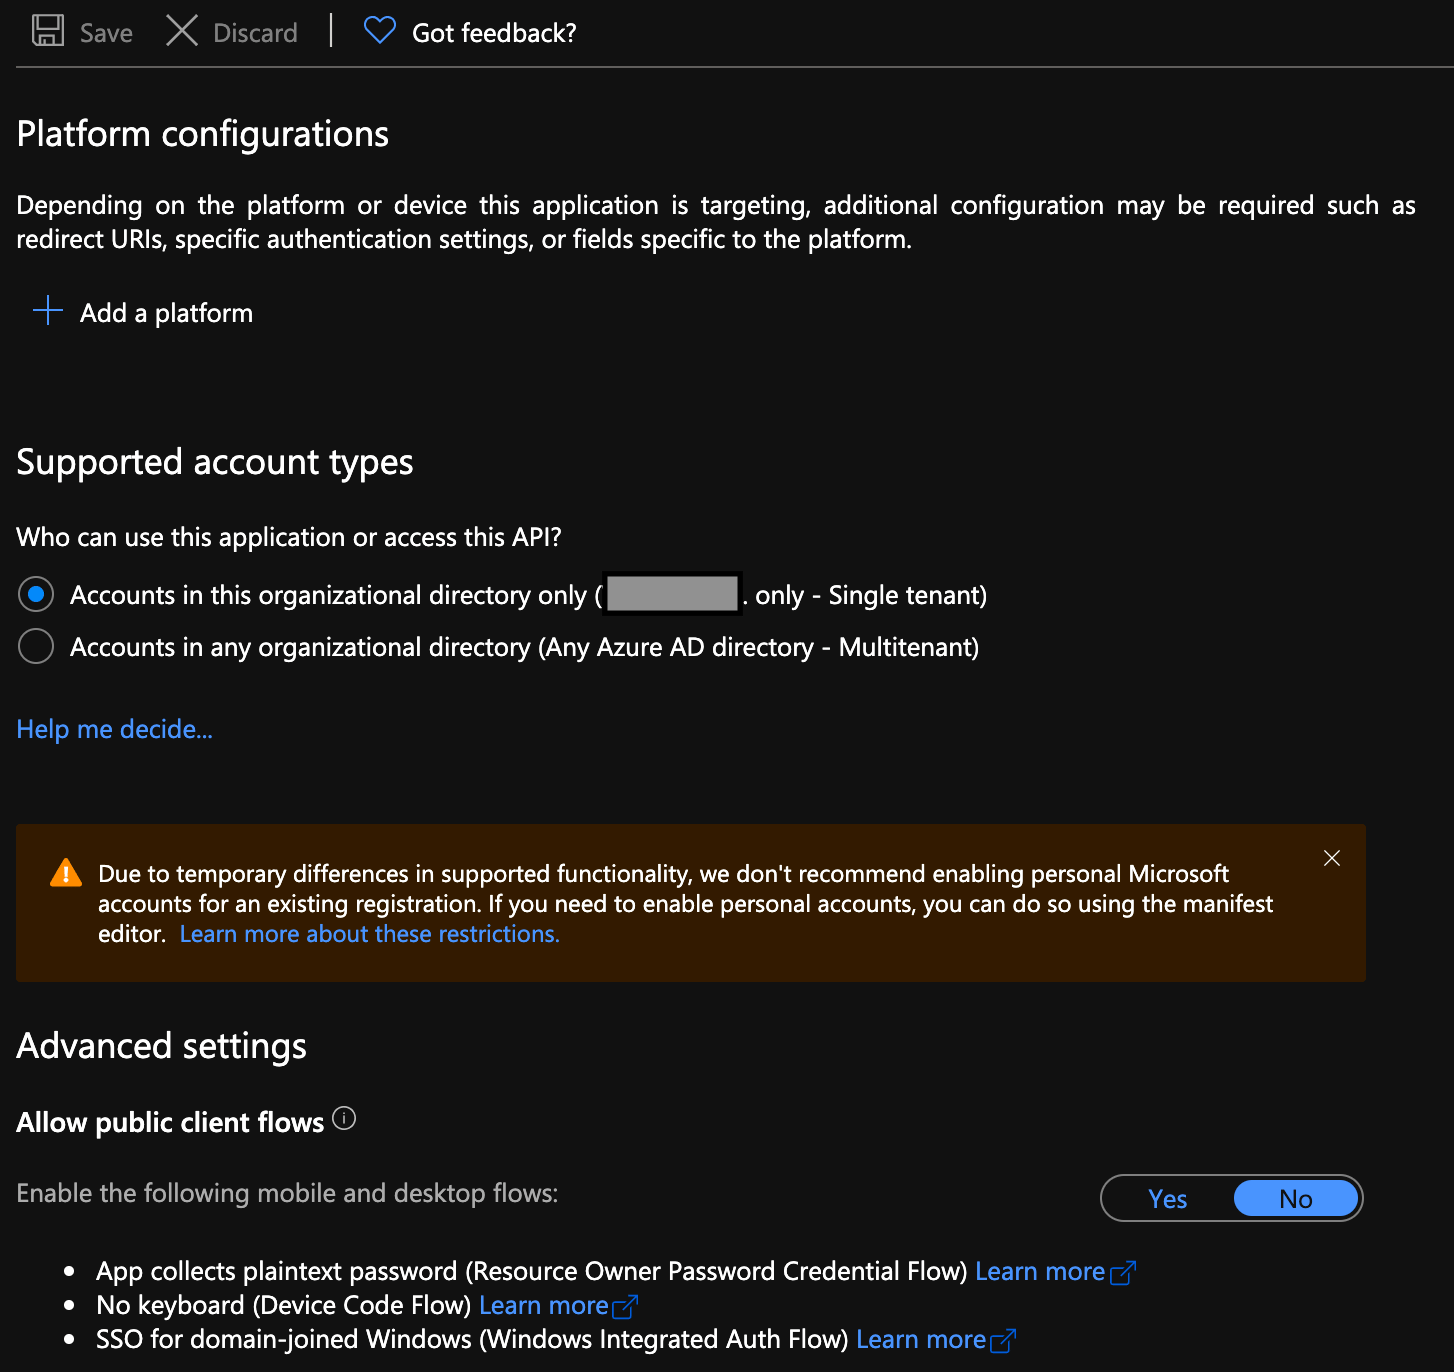 3. Click **Add a platform** under **Platform Configurations**.
The **Configure platforms** panel appears.
4. Click **Web** in the **Configure platforms** panel.
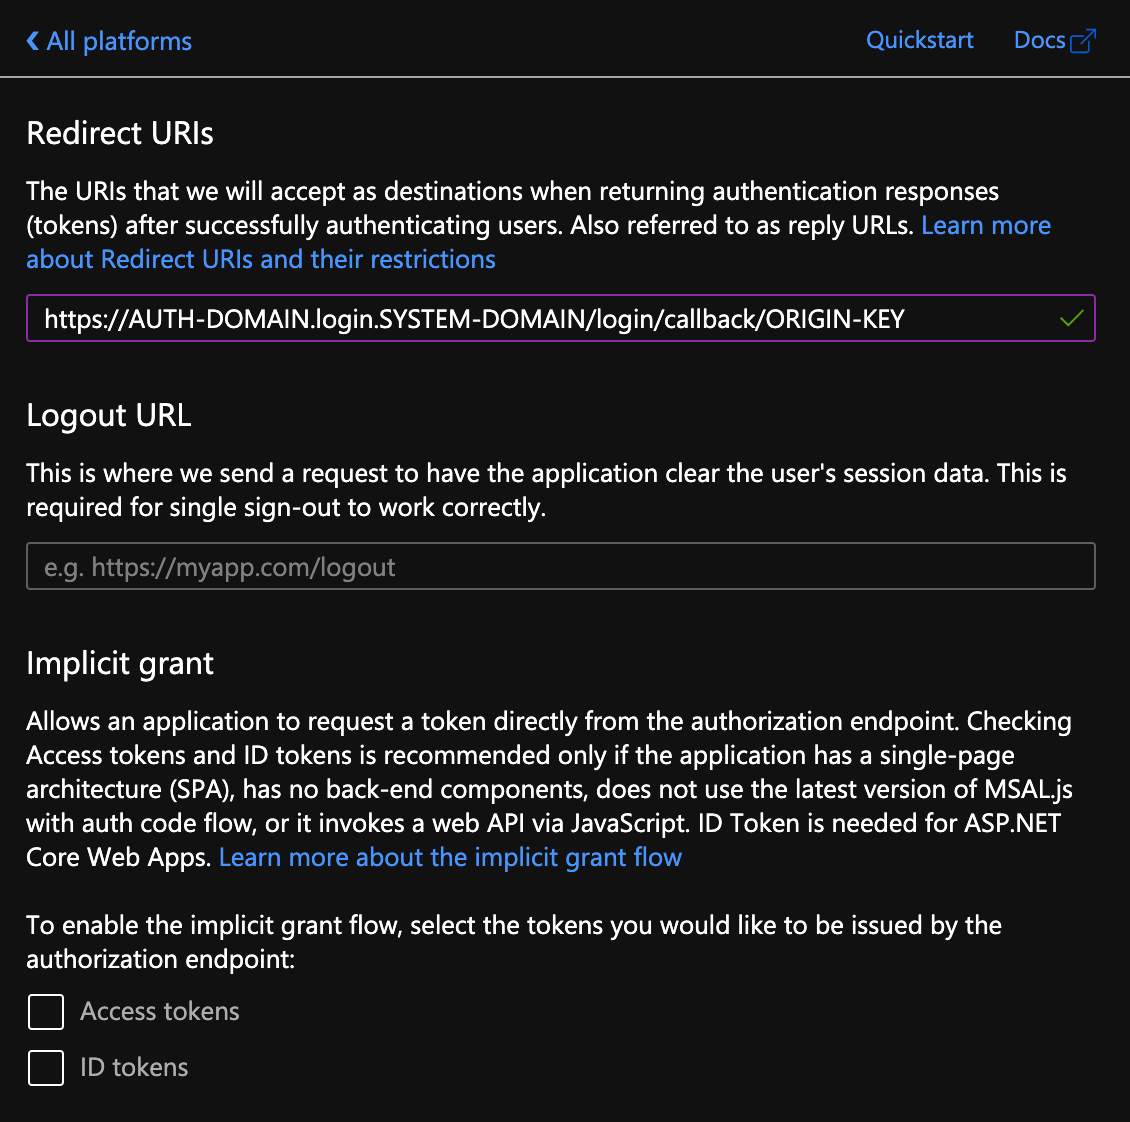
5. Under **Redirect URIs**, enter the following as relevant for either your production or staging implementation:
* **Staging**:
* Vindicia Merchant Portal staging: [https://portal.staging.us-west.vindicia.com/portal/sso\_return](https://portal.staging.us-west.vindicia.com/portal/sso_return)
* **Production**:
* Vindicia Merchant Portal production: [https://portal.vindicia.com/portal/sso\_return](https://portal.vindicia.com/portal/sso_return)
**Note:** Once you add a URI, click **Add URI** to add any additional URIs.
6. Leave the **Logout URL** field blank.
7. Click the **Access Tokens** and **ID Tokens** check boxes in the **Implicit grant** section.
8. Click **Configure**.
 4. Return to the **Overview** page.
5. Click **Endpoints** in the top panel.
6. Copy the **OpenID Connect metadata document** to the .txt file.
7. Return to the **Overview** page.
8. Copy the following values to the .txt file.
* **Application (client) ID**
* **Directory (tenant) ID**
9. Ensure the .txt file contains the following information:
* **Application (client) ID**
* **Directory (tenant) ID**
* **Client Secret**
* **OpenID Connect metadata document**
10. Encrypt the .txt file and pass it to your Vindicia contact point for integration.
11. Add the users that will use Vindicia Merchant Portal to the newly created application in Azure AD.
**Parent topic:**[External User Authentication in Vindicia](../topics/externalUserAuthenticationAbout)
This documentation is built and hosted on [Mintlify](https://mintlify.com), a developer documentation platform.